
-
Guest-to-host heap overflow via integer overflow in VMXNET3 TSO segmentation (CVE-2026-59346)
September 2026 · ZDI-26-647 / CVE-2026-59346 (CVSSv3 9.3 vendor / 7.5 ZDI) · Fixed in VMware Workstation/Fusion 26H1u1 (VMSA-2026-0007) Broadcom shipped a fix for a VMXNET3 TSO overflow last year, CVE-2025-41236. The patch adds four bounds checks to the segmentation function. All four bound individual descriptor fields against a fixed ceiling, and none of them…
-
15-year-old pre-auth nginx RCE across 13 call sites: two-pass capture clobbering (CVE-2026-42533)
CVE-2026-42533 · Fixed in nginx 1.30.4 / 1.31.3 · Affected: nginx 0.9.6 through 1.30.3 (stable) and 1.31.2 (mainline) · NGINX Plus R33-R36 (fixed in R36 P7) and 37.0.0.1-37.0.2.1 (fixed in 37.0.3.1) · F5 Advisory · Reported by Stan Shaw A note for defenders If you run nginx with map directives that use regex patterns, and…
-
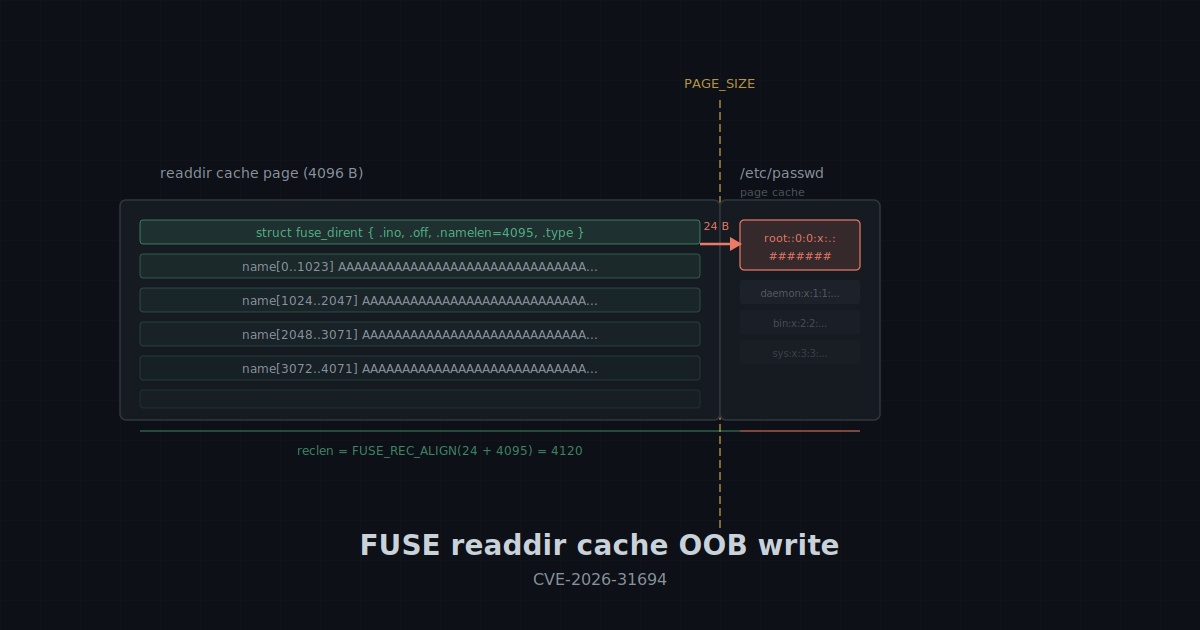
Unprivileged root via an out-of-bounds write in the FUSE readdir cache (CVE-2026-31694)
CVE-2026-31694 · Fixed in mainline (51a8de6), 20 April 2026, Cc: stable · Fixes 69e3455 · Latent since 69e3455 (2018) · Affected: v6.16 through the fix · Reported by Qi Tang and Zijun Hu · Fix authored by Samuel Page In October 2018 Miklos Szeredi added a readdir cache to FUSE, with a bounds check that…
-
Unprivileged root via a use-after-free in DRM GEM change_handle (CVE-2026-46215)
Reported to security@kernel.org, 12 April 2026 · Fixed in mainline (5e28b7b), May 2026, Cc: stable · Fixes 53096728 · Affected: v6.18-rc1 through the fix · CVE-2026-46215 (reported independently; credited to another researcher, see the disclosure section) Puttimet Thammasaeng found this bug before I did, so the upstream Reported-by and CVE-2026-46215 are theirs. I found and…
-
Bounding against the wrong buffer: an OOB read/write in KVM SEV-SNP (CVE-2026-53360)
Reported to security@kernel.org, 8 April 2026 · Fixed in mainline (db3f219), May 2026, Cc: stable · Fixes 4af663c · Affected: KVM SNP host support, ~v6.10 through the fix · CVE-2026-53360 (track commit db3f219 on linux-cve-announce) A malicious SEV-SNP guest can corrupt the host kernel’s heap and learn a good deal about its layout, through the…
-
Guest-to-host escape via QEMU CXL Type 3 mailbox overflows
6th April 2026 · Reported to qemu-security · Classified as non-security (CXL outside policy scope) · Found by manual code audit I spent a few evenings reading QEMU’s CXL Type 3 mailbox handlers by hand, without the static-analysis tooling I use in most of my other writeups, and came out with three bounds-checking bugs in…
-
Use-after-free in CPython’s perf_trampoline via unsynchronised arena teardown
January 2026 · CPython Issue #143228 · Fix PR #143233 · Patched in 3.13/3.14, 3.12 marked Won’t Fix The scanner I wrote to find the Django SQL injection was Python-only. Swapping its graph ingestion from Python’s ast module to libclang took a weekend and left the reasoning core untouched, and the first thing the C…
-
SQL injection in the Django ORM via the Q object connector (CVE-2025-64459)
November 2025 · CVE-2025-64459 (CVSS 9.1) · Fixed in Django 5.2.8, 5.1.14, 4.2.26 I ran a scanner I had been building for my dissertation over the Django source and it came back pointing at one line in the ORM’s query compiler. CodeQL’s default Python suite finds nothing there, and it is right not to, because…